Cyber risk · Forensics · Incident response

Security leadership, built around your risk.

A senior security leader on a fractional basis, for regulated mid-market organisations that need real leadership but can’t justify a full-time CISO — healthcare and biotech, financial services, and organisations operating across the US and EU. If something goes wrong, the same firm that wrote your plan runs your response.

Thirty minutes, no cost, no pitch — a senior second opinion on where your biggest security or compliance gap probably is.

Track record

5,000employees protected across 6 countries
24/7follow-the-sun security operations, built and led
30%faster mean time to respond
0major findings across regulatory and internal compliance reviews

Results from senior security leadership at a NASDAQ-listed, GxP-regulated biotechnology company.

  • HIPAA
  • HITECH
  • GDPR
  • NIS2
  • NIST CSF 2.0
  • HITRUST
  • ISO/IEC 27001
  • SOC 2
  • GxP
  • NIST 800-53
Is this you?

We are usually called in for one of these.

A hospital, payer or enterprise customer has sent a vendor-risk questionnaire, and the deal is not moving until it is answered properly.

An audit is coming — SOC 2, ISO 27001 or HITRUST — or your cyber insurer wants named security leadership before renewal, and nobody can say with confidence what would be found.

The board or audit committee has started asking about cyber risk, and the answers so far have been technical rather than useful.

You run a US parent and an EU subsidiary, and HIPAA and GDPR obligations are currently being handled by two different firms.

Something has already happened, and you need someone who can establish what, prove it, and say so on the record.

You need a CISO's judgement and accountability, but not a full-time CISO's salary — and you want the same person on the worst day.

If more than one of these is true, the free 30-minute call is the right place to start.

What we do

Three practices. One accountable lead.

Security strategy, incident response and assessment work are handled in one place, so the person who advises your board is the person who knows your environment on the worst day.

Fractional vCISO

Executive security leadership on a fixed monthly commitment.

  • Security strategy, roadmap and budget owned at executive level
  • Board and audit-committee reporting a board can act on
  • Policy set, programme governance and metrics
  • Vendor-risk answers for hospital and payer customers, so deals do not stall

Forensics & Incident Response

Retained response, named responders, agreed engagement times.

  • Host, cloud and email forensics: root cause, scope, dwell time
  • Ransomware and business email compromise containment
  • Evidence that stands up with counsel, insurer and regulator
  • Notification analysis: HIPAA/HITECH, GDPR Art. 33/34

Risk & Compliance Assessments

Evidence-based review against the framework your buyers and regulators use.

  • HIPAA Security Rule risk analysis (45 CFR 164.308(a)(1)(ii)(A))
  • NIST CSF 2.0 baseline and HITRUST readiness
  • ISO/IEC 27001 and SOC 2 gap assessments ahead of audit
  • GDPR and NIS2 applicability and gap review
Also

Secure AI adoption

Governance and data-boundary controls so Microsoft 365 Copilot, Claude and other enterprise AI can be rolled out in regulated environments without widening data exposure — acceptable use, DLP and labelling, vendor-risk review and audit logging.

Ask about AI governance

Also available once the core engagement is underway: SOC modernisation advisory, cloud security review (AWS, Azure, GCP), and security awareness training — extensions to the core practice, not the headline.

How an engagement starts

A clear path from first call to ongoing cover.

  1. Free posture conversation

    30 minutes, no cost

    A senior second opinion on where your biggest security or compliance gap probably is — current state, what is actually in scope, and what is driving the timeline. No pitch.

  2. Baseline assessment

    2–3 weeks

    An evidence-based review against the framework your buyers and regulators use, ending in a ranked plan with cost and owner.

  3. Ongoing cover

    Fixed monthly

    A fractional CISO retainer, an incident-response retainer, or both — scoped to a fixed monthly commitment agreed up front.

One practice, both jurisdictions

US and EU obligations, handled in one place.

Not passed between firms. Where a group runs a US parent and an EU subsidiary, the assessment, policy set and playbook are written once and mapped to both.

United States US

  • HIPAA and HITECH
  • State breach statutes
  • HHS Office for Civil Rights expectations
  • NIST CSF 2.0, HITRUST, SOC 2
  • SEC cyber-disclosure readiness for public companies

European Union EU

  • GDPR, including Art. 33/34 notification analysis
  • NIS2 applicability and gap review
  • Member-state health rules
  • ISO/IEC 27001
  • Cross-border transfer governance (DPAs, SCCs)
Written once. Mapped to both.One accountable lead across the Atlantic.
Ransomware readiness

Five things to fix in 30 days.

None of this needs new tooling or a budget cycle. It needs decisions made before the call comes, and evidence that the decisions hold.

  1. Know your recovery time. Prove it.

    Pick the system you cannot run without, ask who would actually be awake to restore it, and time the whole thing end to end.

  2. A backup you have never restored is a file, not a control.

    It is usually the one system nobody monitors — and the one you find out about at the worst possible moment.

  3. The clock starts before you know what happened.

    Notification deadlines run from awareness, not from the day your investigation finishes.

    NIS2 early warning · 24hGDPR notification · 72h
  4. Decide who decides — before the call comes.

    Payment, notification, law enforcement, taking systems offline. Every decision left unmade on the day is a delay.

  5. The first hour is forensic.

    What is done in the first hour decides whether you end up with evidence that holds, or only an account of events.

Thirty days is enough. One tabletop, one restore test, one decision matrix. That is the whole programme — and it is the difference between a bad week and a bad year.
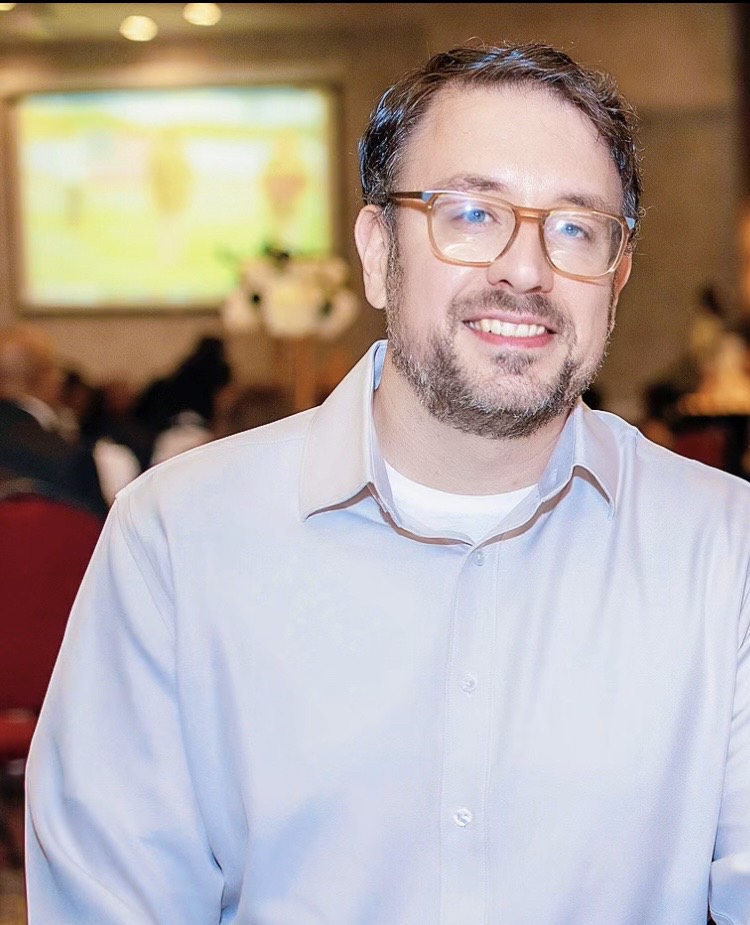
Portrait of Jonathan Tice, Founder, CEO and CISO of JT Cyber Group
Jonathan TiceFounder, CEO & CISO
Who you work with

Senior judgement, named and accountable.

Twelve-plus years across biotechnology, healthcare, financial services and federal government — from writing FISMA and NIST 800-53 frameworks to building a global, follow-the-sun security organisation for a publicly traded, GxP-regulated company.

Jonathan has served as incident commander for Sev-1 events, presented risk to executive leadership, contributed to board-level reporting and SEC disclosure readiness, and been security owner for enterprise AI rollouts. Forensics and incident response are delivered under his direction, engaged per client from a vetted specialist bench — so the same firm that built your plan runs your response.

ISACA CISM CompTIA SecurityX CompTIA Security+
Common questions

What clients ask before the first call.

How does an engagement start?

A free, thirty-minute security posture conversation — a senior second opinion on current state, the obligations actually in scope, and what is driving the timeline. If it makes sense to continue, a baseline assessment follows over two to three weeks, ending in a ranked plan with cost and owner against it. From there you can take a fractional CISO retainer, an incident-response retainer, or both.

Is the first call really free?

Yes. It is a genuine thirty-minute security posture conversation — a senior second opinion on where your biggest security or compliance gap probably is, not a sales demo. Most engagements start here, and there is no cost and no obligation.

How is the work priced?

Ongoing work is scoped to a fixed monthly commitment agreed up front, so there is no hourly meter running and no surprise on the invoice. The free posture conversation is where scope gets established well enough to quote.

Do you handle both US and EU obligations?

Yes, in one practice rather than passed between firms. That covers HIPAA and HITECH, state breach statutes and HHS Office for Civil Rights expectations on the US side; GDPR, NIS2 and member-state health rules on the EU side.

Where a group runs a US parent and an EU subsidiary, the assessment, policy set and playbook are written once and mapped to both.

Which frameworks do you assess against?

Whichever one your buyers and regulators actually use:

  • HIPAA Security Rule risk analysis (45 CFR 164.308(a)(1)(ii)(A))
  • NIST CSF 2.0 baseline and HITRUST readiness
  • ISO/IEC 27001 and SOC 2 gap assessments ahead of audit
  • GDPR and NIS2 applicability and gap review
A customer has sent us a vendor-risk questionnaire. Can you help?

Yes. Answering hospital and payer vendor-risk reviews properly, so deals do not stall, is part of the fractional CISO engagement. It is one of the most common reasons we are brought in.

What happens if we have an incident?

On a response retainer you get named responders and agreed engagement times rather than a queue. The work covers host, cloud and email forensics to establish root cause, scope and dwell time; ransomware and business email compromise containment; and evidence that stands up with counsel, your insurer and a regulator.

Notification analysis under HIPAA/HITECH and GDPR Articles 33 and 34 is handled as part of the same engagement, not billed as a separate project.

Can you help us adopt AI without widening our data exposure?

Yes. That includes acceptable use and governance frameworks, sensitivity labelling and DLP so AI-surfaced content honours least-privilege boundaries, vendor and data-handling review covering retention and model-training terms, and SSO, role-based tiers and audit logging. This has been done at enterprise scale for Microsoft 365 Copilot and Claude in a regulated, publicly traded environment.

Something not answered here? Ask on the free call

Start here

Book your free 30-minute security posture conversation.

Tell us what is driving this. We will come to the call having read it, and leave it with a clear view of what is in scope and what to do first — no cost, no pitch.

You getThe founder, not a junior — on both sides of the Atlantic.
Active incident?Email with INCIDENT in the subject line.
There is a problem with this form

    Please enter your name.

    Please enter a valid email address.

    Please do not include sensitive incident details or personal health information in this form.